


Secure Remote Access for OT & IoT Operations
One Zero Trust platform. Clientless ZTNA, remote browser isolation, and containerized apps on Kubernetes — for safe, browser-based access to critical industrial environments, without VPNs or jump servers.
Join over 5,000 leading companies that trust Cybele Software
















Safe, isolated access for every OT operator and vendor
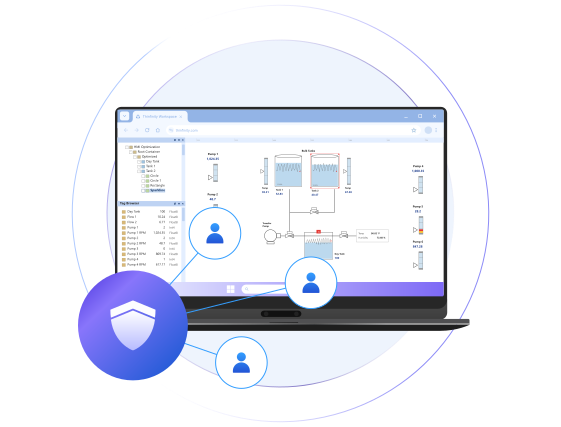
Give operations teams real-time, context-driven visibility into cyber-physical systems through one governed platform — without compromising security or control.
Clientless & browser-based
HTML5 access from any device — no plugins, agents, or endpoint changes.
Isolated by default
Sessions are brokered and encrypted; OT assets are never exposed to the user's network or device.
Unified operational view
SCADA dashboards, HMIs, and apps brokered into one governed workspace.
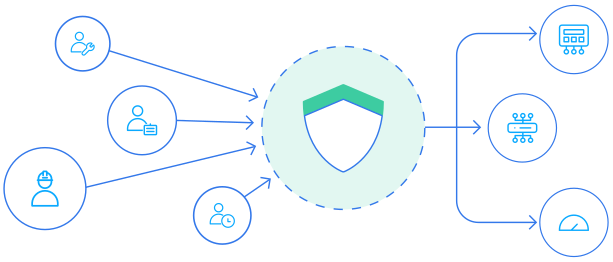
People -> Policy -> OT Assets
Operators / Vendors / Engineers
Thinfinity Broker. Identity & policy.
Secondary Broker / Agent in OT zone
SCADA / PLC / RTU / HMI
Why traditional OT remote access fails
VPNs and jump servers fail in OT because they place users on the network and create standing, broad access that ignores the Purdue Model.
VPNs break segmentation
They extend the network to the user and flatten the IT/OT boundary that IEC 62443 zones-and-conduits require.
Jump servers are a target
A hardened jump host is still an exposed host to patch, monitor and defend — and still relies on inbound exposure.
Credentials = unrestricted access
Standing access means one phished account can reach critical assets and move laterally toward controllers and HMIs.
Visibility into your systems to reduce downtime and operate safely
Industrial operations demand constant visibility to maintain safety, uptime, and efficiency. Disconnected tools and blind spots increase operational risk, production loss, and regulatory exposure. Thinfinity unifies access to OT, IoT, and enterprise systems under one governed Zero Trust layer.
Unify, don't rip-and-replace
Brokers existing OT, IoT, and IT systems into governed sessions under one policy set.
Govern every interaction
Identity-based access with full observability down to the device level.
Respond & restore faster
Just-in-time access shortens MTTR for break-fix and emergency events.
Shrink the attack surface
No permanent tunnels, no open inbound ports, no lateral movement.
4 ways
Thinfinity governs OT & IoT access
Secure Managed Access
A controlled, policy-driven access model for internal and external users — browser-based access to apps, devices, and operational systems with no changes to networks, protocols, or legacy infrastructure.
Multi-Protocol Legacy Coverage
One access layer for RDP, VNC, SSH, Telnet, TN3270/5250, and Thinfinity VNC — from Windows SCADA workstations to AS/400-connected plant systems and embedded HMIs.
Privileged Access & Maintenance
RPAM-style supervised access for patching and maintenance windows — read-only or full control per user, with session recording and policy-driven change control while remediation is pending.
Third-Party & Vendor Access
Grant limited, time-bound access to integrators and OEM vendors without VPNs or permanent tunnels. Every session is identity-enforced, recorded, and scoped to approved resources only.
The growing need for safe, immediate OT & IoT access
OT/IoT environments sit where cybersecurity, physical safety, and uptime collide. The stakes are higher, the systems are older, and the access demands are relentless.
Safety-critical access
Outages and break-fix events demand fast access — but permanent tunnels and unmanaged endpoints raise exposure.
Distributed teams & complexity
Global vendors, contractors, and remote staff need access across many sites and time zones.
Legacy OT, modern threats
Systems never built for modern connectivity now face an expanded attack surface.
Rising compliance & audit
NERC CIP, IEC 62443, NIS2, and more demand controlled, auditable access.
Experience OT/IoT access
without the risk
Thinfinity streams desktops, apps, and industrial dashboards through isolated, brokered sessions. OT and IoT systems stay protected in their environment — never exposed to the user's device or network, and data movement is policy-controlled.
No open inbound ports
Reverse gateway over an outbound SSL/TLS tunnel — no inbound ports into OT (gateway terminates HTTPS/443).
No direct connections
Users never touch devices; the Broker mediates every session.
Data movement is policy-controlled
Clipboard, file transfer & device redirection are policy-controlled — disable per profile.
Key benefits for OT & IoT teams
Built for OT, IoT & ICS operations
Incident response & training
Deliver safe workspaces for response, investigation, and OT cyber readiness without touching live systems.
Remote operations & monitoring
Stream SCADA dashboards, HMIs, and IoT sensor analytics into isolated sessions for engineers and operators.
Vendor & contractor access
Grant limited, time-bound access without exposing internal networks or opening permanent tunnels.
Troubleshooting & field maintenance
Let technicians safely reach OT environments from unmanaged or personal devices without contaminating production networks.
Compliance-aligned platform capabilities
Thinfinity supports the implementation of access, isolation, and audit controls required by leading industrial and security frameworks:
IEC 62443
NERC CIP
NIST 800-82
NIST 800-53
NIST CSF
ISO 27001
NIS2 (EU)
CIS Controls
CMMC L2
SOC 2 Type II
Attestations & shared-responsibility note
Cybele Software holds SOC 2 Type II (available under NDA). GDPR, HIPAA, and ISO 27001 alignment is inherited/configurable through the chosen infrastructure deployment. Certification depends on how controls are implemented and maintained by your organization.
The complete OT/IoT access capability stack
Everything in a single governed platform — no stitching together separate point tools for isolation, containers, virtual desktops, and remote access.
Clientless ZTNA + multi-protocol broker
RDP · VNC · SSH · Telnet · TN3270/5250 + Thinfinity VNC, brokered with no in-network IP exposure.
Remote Browser Isolation (RBI)
Disposable remote browsers for risky web and SaaS — no website code touches the endpoint.
Containerized app streaming on K8s
Stream containerized apps and desktops on Kubernetes — OKE, AKS, EKS, GKE, or on-prem clusters.
VDI & DaaS with autoscaling
Provision and scale virtual desktops and apps via Cloud Manager across cloud and on-prem.
Zero Trust by design + full audit
Identity-based access, no inbound ports (reverse gateway), session recording and analytics.
Deploy anywhere, no lock-in
On-prem, air-gapped, or OCI / Azure / AWS / GCP / IONOS, managed from one dashboard.
How OT & IoT teams use Thinfinity
Just-in-time vendor access
Temporary sessions for emergency maintenance with no permanent network pathways.
Granular access to PLC, RTU, HMI
Controlled access to operational resources without exposing backend networks.
Isolated access for field engineers
Supports BYOD/BYOA without risking malware or data leakage.
Segregated IT/OT networks
Ensure IT and OT never directly connect while still enabling safe access.
Unified operational workflow
View data, raise tickets, communicate, and resolve incidents from one secure platform.
Measurable OT/IoT outcomes
+5000
companies trust Thinfinity technology
0
open inbound ports or permanent tunnels
1
governed platform — one pane of glass
100%
clientless, browser-based access
Industries we serve
Energy & Utilities
Generation, grid, DER, water
Manufacturing
Plant floor, OEM & integrator access
Government & Defense
Critical infrastructure, sovereign sites
Transportation
Rail, ports, logistics & signaling
Healthcare
Biomed devices & facility systems
Oil, Gas & Mining
Remote, offshore & constrained sites